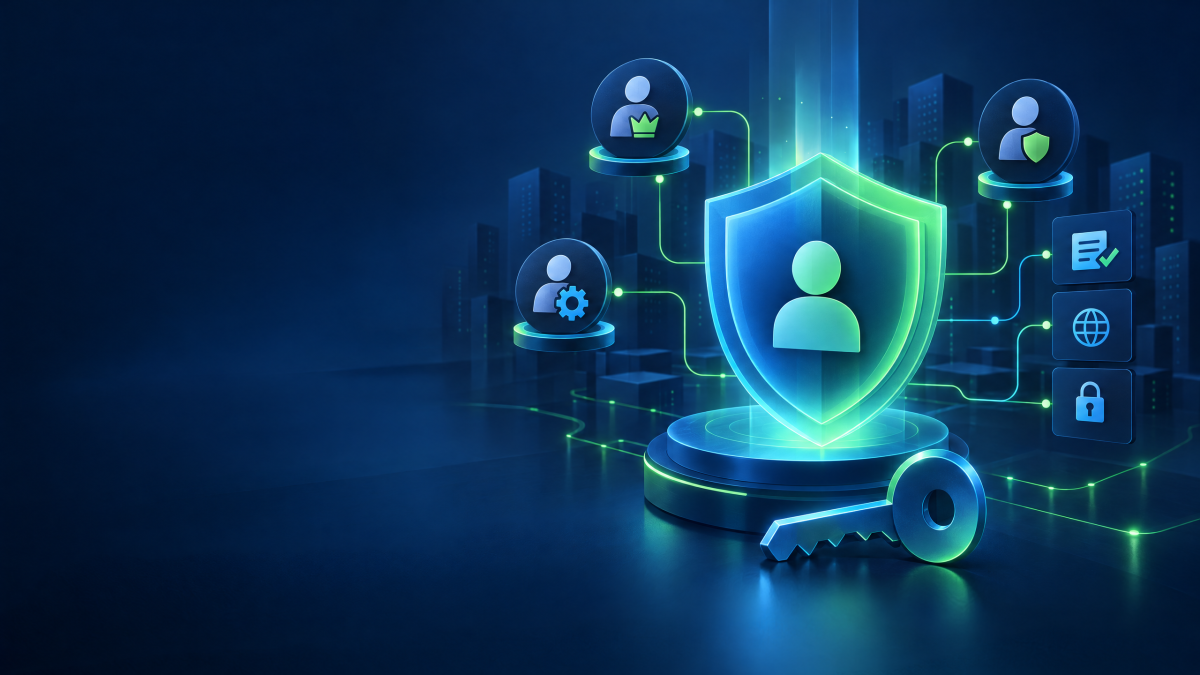
Microsoft is extending Project Perception to secure enterprise AI agents as organizations give software systems access to data, applications and business processes. The company’s approach treats an agent as a separate security subject with its own identity, permissions, runtime and risk—not simply as an extension of the employee who launched it.
Why agent security is different
Microsoft argues that agents are non-deterministic: their outputs and plans can change as context changes, and they may operate continuously at machine speed. An agent can also be manipulated by untrusted content or compromised through the tools and data it can reach.
The central design principle is to keep authority outside the model. Controls should determine what an agent can access and whether it can continue operating, rather than asking the model to police its own behaviour.
What Project Perception adds
Microsoft says its security stack will discover more local agents, bringing the total to 60 supported local agents, and give them durable identities through Microsoft Entra Agent ID. That identity is intended to anchor ownership, lifecycle, permissions, authorization and policy.
The company is also introducing Dynamic Permissions. Agents can start with no authority, receive only the access required for a specific task, and lose that access when the task changes or ends. Higher-impact actions can require verified human approval.
Dynamic Agent Risk combines signals from identity, data, endpoints, cloud, network, runtime and agent activity. Dynamic Conditional Access can then respond proportionately: preserve reads while blocking writes, narrow reachable resources, shorten access, require approval, isolate the runtime or stop execution.
Guardian Agents are a second layer of automation
Microsoft says Guardian Agents and security playbooks will investigate evidence, recommend or apply containment, and help harden policy as risk changes. People retain control of objectives, approval boundaries and consequential decisions; the Guardian Agents handle continuous work that would not scale through manual triage.
This is not a claim that autonomous security removes the need for human governance. It adds another automated decision layer, which itself needs auditable policies, clear escalation paths and testing against false positives. Organizations should be cautious about allowing one set of agents to grant or revoke authority to another without independent controls.
What businesses should take from the announcement
The practical message is that traditional identity and least-privilege controls need to be extended to non-human operators. Businesses deploying agents should maintain an inventory, assign accountable owners, separate agent identities from user identities, restrict tool and data access, and log actions at a level that supports investigation.
Microsoft’s proposal is closely aligned with the security problem described in our earlier coverage of AI agents entering commercial workflows: once software can take actions on behalf of a user or organization, access boundaries matter as much as model quality.
Project Perception is therefore best understood as an architectural direction and a Microsoft product strategy, not proof that agent risk has been solved. The hard test will be whether these controls work across mixed vendor environments and remain understandable to the people responsible for approving them.